 Written by
Data protection – compensation – practical guidance
When an organisation loses or exposes your personal data, the Information Commissioner can investigate and fine – but cannot award you a penny. Compensation comes only from a civil claim, and the courts have spent the last five years defining exactly what that claim demands: proof of infringement, proof of damage, and a causal link between them. This is the route, the evidence, and the realistic numbers.
Snapshot
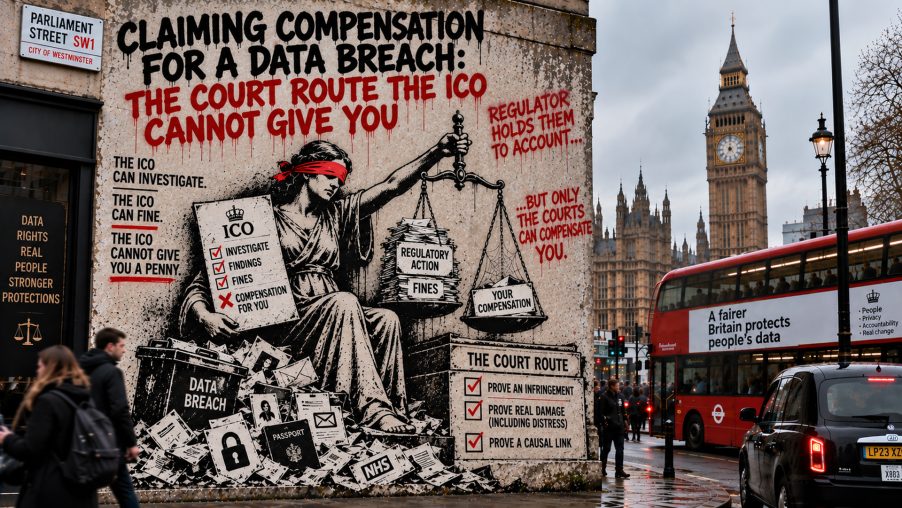
The ICO and the county court do different jobs. The ICO can investigate a breach, record its view and fine the organisation, but compensation for the victim exists only in the civil courts, under Article 82 of the UK GDPR as supplemented by the Data Protection Act 2018 – and only where the claimant proves an infringement, real damage (which expressly includes distress) and causation. Lloyd v Google has closed the door on mass opt-out claims without individual proof, and the courts treat trivial or low-value claims accordingly. Knowing which route fits your breach – complaint, claim, or both – is the first decision worth getting right.
What the ICO can do – and the one thing it cannot
The Information Commissioner’s Office is a regulator, not a compensation scheme. It can investigate complaints, and for the gravest infringements of the UK GDPR it can impose administrative fines of up to £17.5 million or four per cent of an undertaking’s worldwide annual turnover, whichever is higher. Those are serious powers, and an ICO investigation can produce a documented, independent view of whether the organisation broke the law.
What the ICO cannot do is order the organisation to pay you anything. The ICO says so in terms: it cannot award compensation, even where it has given its opinion that an organisation has broken data protection law. An ICO decision letter is not money in your pocket. It is, at most, evidence: the ICO’s guidance notes that you can give its letter to a court, but the court will make its own decision, which may not agree with the ICO’s view.
That distinction matters, because an upheld ICO complaint is easy to mistake for a judgment. It is not. The complaint route produces accountability; the compensation route produces money; and only the second is a court claim.
The court route: Article 82 and section 168
Article 82(1) of the UK GDPR gives any person who has suffered material or non-material damage as a result of an infringement of the Regulation the right to receive compensation from the controller or processor for the damage suffered. The controller is liable for damage caused by processing that infringes the Regulation; a controller or processor escapes liability only if it proves it was not in any way responsible for the event giving rise to the damage. The right, in other words, is statutory, direct and enforceable against the organisation itself – not mediated through any regulator.
The scope of “damage” was deliberately widened by Parliament. Section 168(1) of the Data Protection Act 2018 provides that, in Article 82, “non-material damage” includes distress. A claimant does not need to show lost money. Distress – anxiety, upset, worry about what has been done with the data – is a recognised head of damage in its own right. That is the express legislative answer to the assumption that data breach claims are only for people who have been defrauded.
Key distinction. An ICO complaint asks a regulator to police the organisation. A civil claim asks a court to compensate the victim. They are not alternatives to be chosen between on convenience – they do different things, and many breaches justify both.
What a claimant must prove
The Supreme Court has defined the proof burden precisely. In Lloyd v Google LLC, Lord Leggatt held that compensation under the data protection legislation requires proof, in each individual case, both that there was unlawful processing of that person’s data and that the person suffered damage – financial loss or distress – as a result. The infringement itself is not compensable: “loss of control” over personal data, without proof of damage caused by it, does not found a claim. Three elements must therefore line up: an infringement, real damage, and a causal connection between the two.
There is also a floor beneath the whole regime. The courts apply a de minimis threshold: a claim below the level of seriousness that the law recognises can be struck out or met with summary judgment, and Rolfe v Veale Wasbrough Vizards LLP – a claim over a single email about school fees sent to the wrong person, who confirmed they had deleted it unread – is treated in the later case law as the example of a claim beneath that threshold. In Stadler v Currys Group Ltd the High Court confirmed that this non-trivial threshold applies to Article 82 claims, while refusing to strike out a claim about an unwiped smart television precisely because the pleaded facts, if true, were not trivial. The practical consequence is that the breach must be worth suing over: a one-off administrative slip, quickly remedied, will struggle.
Identify what the organisation did or failed to do, and which duty it breached – the breach notification letter, your own records and any ICO view all belong here.
Document what you actually suffered: financial loss with bank records, or distress described concretely – what you felt, for how long, with what effect on sleep, work or health.
Connect the two. Distress caused by other events in your life is not compensable; the court compensates only the damage the breach caused.
Lloyd v Google and the mass-claim dead end
Lloyd v Google was an attempt to recover compensation for more than four million iPhone users whose browsing data had allegedly been collected without consent, through a single representative claimant, without any of them having to prove individual damage. The Supreme Court rejected it. Damages under the data protection legislation compensate an individual for damage that individual has suffered, and that assessment cannot be made on a common, “lowest common denominator” basis across a class; where each person’s entitlement turns on their own circumstances, an opt-out representative action cannot recover compensation for them.
The judgment did not abolish collective redress – a representative claim can still decide common issues, and group litigation remains available – but it destroyed the economics of the no-proof mass claim. Every person who wants compensation must be able to prove their own damage. For the individual litigant, that is actually the useful lesson: your claim stands or falls on your own evidence, not on the scale of the breach in the news.
Realistic quantum and the costs risk
How much is distress worth? The honest answer is: far less than the internet suggests, and it depends on the facts. The ICO’s guidance is that the judge will take into account all the circumstances, including how serious the infringement was and its impact on you, particularly when assessing distress. On that approach there is no fixed tariff: everything turns on the facts of the case.
The large numbers that circulate come from a different world. The highest privacy awards yet made by the English courts – between £72,500 and £260,250 in Gulati v MGN Ltd – compensated victims of years of repeated voicemail interception by national newspapers, an aggravating scale of intrusion no ordinary data breach resembles. At the other end, in Stadler the High Court observed that a single-incident breach claim might end up being worth “just a few hundred pounds”. Most distress-only data breach claims live much closer to Stadler than to Gulati.
There is a costs discipline attached. If a claimant fails to demonstrate damage or distress, the court will not award compensation and can order the claimant to pay the other side’s costs. A weak claim is not a free shot. On the small claims track that exposure is limited, but issuing a claim you cannot prove still costs the issue fee, the time, and the risk of a judicial finding that the claim was trivial.
Where to issue: small claims and the privacy-tort alternative
For an individual claim of realistic value, the forum is the County Court. The Civil Procedure Rules make the small claims track the normal track for any claim valued at not more than £10,000. That is where a distress-only data breach claim of realistic value belongs: informal, and designed to be used without legal representation. Issuing in the High Court is not a way to add gravitas – in Stadler the judge could see no reason the claim had been issued there and transferred it to the County Court, by which point the two sides had run up combined costs in five figures on a claim the judge said might be worth just a few hundred pounds.
Some breaches also support a claim for misuse of private information, the common-law privacy tort. The tort differs from the statutory route in two ways that matter. First, it can compensate the misuse itself, without separate proof of distress – that is how the Gulati awards were built. Second, it requires a positive misuse of private information: in Warren v DSG Retail Ltd the High Court held that a negligent failure to keep data secure, without any use of the information by the defendant, does not amount to misuse of private information or breach of confidence. A hacker breaking in, or an employer losing files, is a data protection claim; an organisation deliberately exploiting or exposing your private information may be both.
Forum discipline. Value the claim honestly first. A distress-only claim from a single breach is a County Court small claim; the privacy-tort route adds value only where the facts show a real misuse of private information, not merely a security failure.
Court claim, ICO complaint, or both
The sensible sequence starts outside the courts. The ICO’s guidance is to raise the matter with the organisation first: compensation can be agreed and paid without any claim at all, and the court will want to know what steps you took to settle before proceedings – in England and Wales, the rules on pre-action conduct apply. A letter before claim that sets out the infringement, the damage and the amount sought can resolve the dispute without any proceedings at all.
An ICO complaint remains worth making in parallel where the breach is systemic, where other people are affected, or where you want the regulator’s independent view on record – that view can later be put before the court. But it should be made in the knowledge of what it is: an accountability measure, not a payment mechanism. If what you want is compensation, the claim is the route; if what you want is the organisation stopped, the complaint is the route; most serious breaches justify both, run in the right order and on a realistic view of what each can deliver.
Source anchors
These anchors support the legal framework described in this article. They do not determine the outcome of any individual claim, which turns on its own facts and evidence.
Primary legislation. The right to compensation and liability, and the administrative fining powers exercised by the Information Commissioner.
Primary legislation. Compensation for contravention of the UK GDPR; non-material damage expressly includes distress.
Reported judgment. Compensation requires proof of individual damage caused by the infringement; no mass opt-out claim without it.
Regulator publication. What to do when an organisation has not kept your information safe, including the limits of the ICO’s powers.
Procedural rules. Track allocation, including the small claims track as the normal route for claims valued at not more than £10,000.
The closing point
The compensation route is real, but it is evidential, not automatic. The ICO’s finest letter will not pay you, and the largest headline awards do not describe the ordinary claim. What wins these cases is unglamorous: a provable infringement, honestly described damage, a causal link between them, and a forum chosen to fit the value of the claim. Get those four things right and the law does the rest.
Data breach route decision point
Get a free written assessment of the route
Legal Lens can structure a preliminary written review of a data breach matter: whether the facts support an Article 82 claim, what the evidence needs to show, and which route – complaint, negotiated settlement or court claim – fits the value and the facts.
ICO complaint, letter before claim, small claims track or the privacy-tort route – matched to the breach and what you want out of it.
What your infringement, damage and causation case needs to contain before any claim is worth issuing.
Assessment outputs
The infringement, the duties engaged, and the routes open on the facts.
The documents and chronology needed to prove damage and causation.
Independent Legal Lens consultancy. Legal Lens is not a regulated solicitors’ firm. A preliminary assessment is not a substitute for regulated legal advice where that is needed.